This tutorial shows how to build and test two B2B journeys in the Admin Portal, using Mosaic-hosted screens:
- Invite journey: registers authenticators when a member follows an invitation link. The link identifies the member and their organization.
- Login journey: collects the member's email, resolves their organization, and authenticates them using its configuration.
Complete the B2B setup through Set members. For these examples, make sure you have:
- A Mosaic application with Application URI for inviting members and Client for inviting members configured. See Configure the invite flow.
- A login client set to Journey-orchestrated, with Login screens set to Hosted by Transmit Security on its SSO client group. See Configure app & client.
- An organization linked to the application, with at least one member email domain registered. See Create organizations.
- Authentication methods and enrollment requirements configured for the application, and a test organization that uses Mosaic authentication methods. See Configure B2B authentication settings and Configure org authentication.
Use a test member whose email matches one of the organization's registered domains. The invite example uses the application's authentication methods so you can test authenticator registration. For federated organizations, Register Member Authenticators completes without presenting registration screens.
Use the journeys you created during B2B setup. Check that each is selected in the appropriate field:
- Invite journey: go to Applications > your app > B2B settings, and check B2B invite journey.
- Login journey: go to Applications > your app > Clients > your login client > Login Experience, and check the SSO Client Group and Journey selected for Journey-orchestrated login.
If either journey doesn't exist yet, select + Create new journey in its field, provide a Name, set Journey's context to B2B, and select Apply. This creates a blank journey and selects it in the field. Save the application or client settings after making changes.
Go to B2B Identity > Journeys and open the invite journey selected in Step 1. Build this flow:
Connect Start to a Register Member Authenticators step and configure:
- Identifier source: leave The user is already authenticated selected (default) to use the member identified by the invitation link.
- Organization (Email or Domain):
@organizations.current().domains[0], the first domain of the organization provided by the invitation link. See Org context. - Failure behavior: leave the default behavior that proceeds to a failure branch.
Connect its Success branch to a Display Information step. Set Message Title to
Registration complete, Message Text toYour authentication methods are ready to use., and Continue Button Caption toContinue.Connect Display Information to Complete Journey.
Connect the Failure branch of Register Member Authenticators to Reject Access.
Select Save.
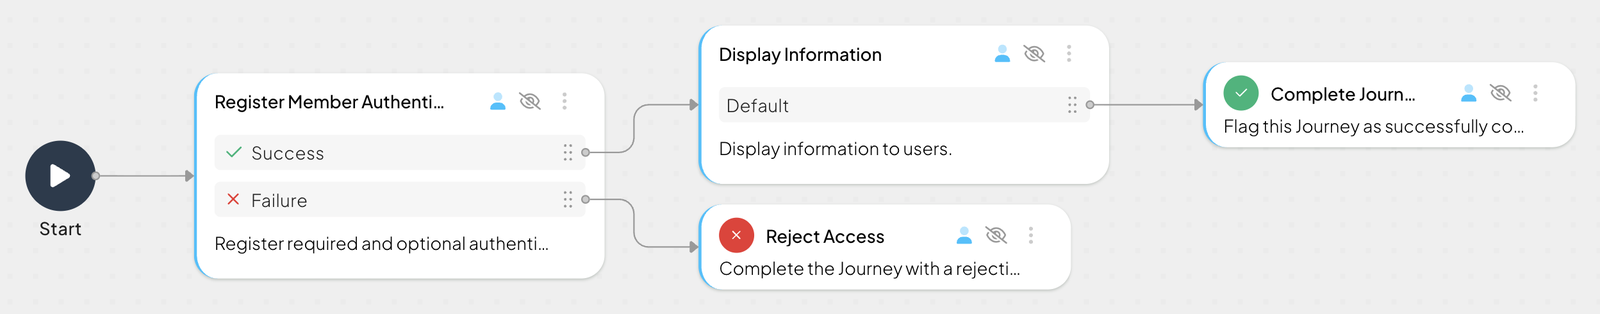
Register Member Authenticators reads the application's enrollment requirements at runtime and skips methods the member has already registered. Changing those requirements changes what the same journey asks members to register.
For example, suppose the application requires password and passkey registration and offers TOTP as optional. A member who already has a password is asked to register a passkey, then offered TOTP with the option to skip it. The step succeeds once the member registers the passkey and either registers or skips TOTP.
To collect details such as the member's name during onboarding, add Collect Information before Register Member Authenticators. You can personalize Form title with Welcome to ${@organizations.current().name}. Use the collected values in an Update User step to save them to the member's profile.
Open the login journey selected in Step 1. In this example, Collect Information collects the email address, and Authenticate Member uses its domain to resolve the organization before presenting the authentication screens.
Connect Start to a Collect Information step and configure:
- Step ID:
collectEmail. - Form title:
Sign in. - In the form builder, add a required email field with item name
emailand a button to submit the form. - Branch output variable:
loginForm, so later steps can read the submitted email asloginForm.email.
- Step ID:
Connect its default branch to an Authenticate Member step and configure:
- Organization (Email or Domain):
loginForm.email, so the organization is resolved from the collected email's domain. - Identifier source: User identified prior to step.
- Identifier type: Email.
- Identifier:
loginForm.email. - Failure behavior: leave the default behavior that proceeds to a failure branch.
- Organization (Email or Domain):
Connect its Success branch to Complete Journey.
Connect its Failure branch to Reject Access.
Select Save.
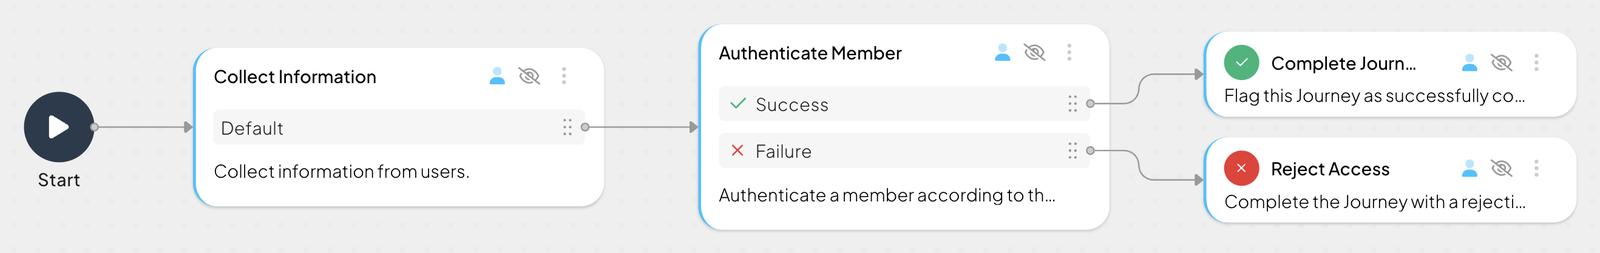
Authenticate Member presents the application's authentication methods or redirects to the organization's Identity Provider, according to the organization's configuration. It handles MFA when required and prompts members with access to multiple organizations to select one after authentication. The same login journey supports both authentication configurations.
If the organization can't be resolved, sign-in fails. On success, the step sets the resolved or selected organization on the journey context.
The login example authenticates existing members. If you want to let new members sign up using the application's authentication methods, extend Collect Information to collect the sign-in or sign-up choice and the required member details. Route sign-up to a separate branch that creates the member before Authenticate Member, and include any required authenticator registration in that branch.
Before testing login, connect your customer-facing application to Mosaic SSO using the protocol configured on your client.
- In the Organization admin portal, select your test organization and application, open Members, and select + Add member. Use an email address you can access at one of the organization's registered domains.
- Assign Organization member and any application roles needed for the test. Select Send invitation to user and save.
- Open the invitation email and follow the link. Check that the registration screens match the application's enrollment requirements: outstanding required methods appear first, followed by optional methods that can be skipped.
- Complete registration and select Continue on the confirmation screen. Check that you are redirected to the configured Application URI for inviting members, with an authorization code your backend exchanges for tokens.
You can also send the invitation from the Admin Portal. See Set members.
- Start login from your application in a fresh browser session so an existing SSO session doesn't skip authentication.
- Enter the invited member's email. Check that the authentication methods shown match the application's sign-in configuration.
- Authenticate using a method registered during the invite journey. Complete MFA if prompted, then check that the flow returns to your application with a successful authentication result.
If your setup includes these cases, also check:
- Multiple organizations: a member with access to several organizations is prompted to select one after authentication.
- Federated login: a member of a federated organization is redirected to its configured Identity Provider.