Follow the steps below to configure this scenario. The linked guides provide additional field descriptions and implementation details.
Real-life example: Acme Group owns a retail bank and a separate brokerage brand. For regulatory reasons, the two brands keep customers, credentials, and policies apart. A customer of both creates two accounts, and signing in to the bank doesn't sign them in to the brokerage.
Use case: two or more apps with their own user pools. Users have a separate account and credentials for each app. Signing in to one app does not sign them in to another.
Resulting structure: one Mosaic application for each isolated user pool. Each one has its own clients, authentication settings, and SSO client groups.
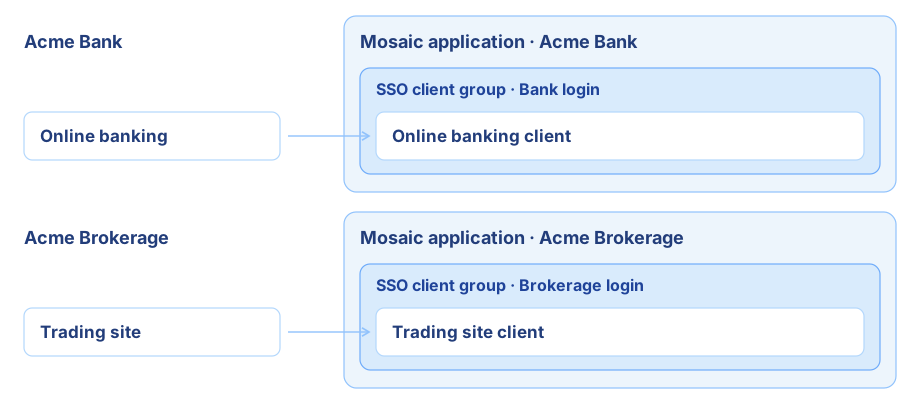
See Choose a setup for your use case to compare all setups.
Decide which apps need their own user pool. Apps that share users belong to the same Mosaic application. See Plan your integration structure.
In the Admin Portal, go to Applications and create a separate Mosaic application for each isolated user pool. For two apps, create two Mosaic applications. See Create Mosaic applications.
Each Mosaic application has its own user accounts and credentials. A user registered in one Mosaic application must register independently in the other.
Mosaic keeps one unified person record per real user at the tenant level, linked to these accounts. Centralized user management doesn't share credentials or sessions between Mosaic applications. See Tenant.
Configure each Mosaic application separately. In each one:
Configure the authentication methods. In its Authentication methods tab, configure the login methods for that app. See Customize login methods.
Create the SSO client group. Skip this for a Mosaic application whose clients all use backend-based login. In Applications > Application > Clients > SSO client groups, select + Add SSO client group, and configure:
- SSO client group name: a name that identifies the group.
- Login screens: Hosted by Transmit Security for Mosaic-hosted pages, or Self managed (Custom UI) for a page you host.
- Login page URL: for self-managed screens, the address of the page you host. For hosted screens, Mosaic generates the URL; to show users a URL on your own domain, enter a custom login page URL. See Configure custom domains.
- Session timeout: how long the group's session stays valid. Default: 14 days, up to 1 year.
Save the group. Each Mosaic application has its own SSO client groups, and its clients select groups only from it, so sessions are never shared across Mosaic applications. See Configure SSO.
Create the SSO journey. In B2C or B2B Identity > Journeys, select Add blank journey and choose SSO-Journey. Build the login flow with the authentication methods configured for that Mosaic application, then save the journey. The Journeys section of Configure SSO explains where SSO journeys are created and how clients select them.
For a step-by-step example using Mosaic-hosted screens and email OTP, follow Create an SSO journey with the Mosaic-hosted experience. Adapt the journey by adding or replacing steps to match your authentication methods and login requirements.
In each Mosaic application, go to Clients, select + Add client, and choose User authentication client. Add the clients for that app under its own Mosaic application. For each client, complete the wizard in the tab that matches its type.
- General: enter the client name and description.
- Authentication flow: leave Does your login use OIDC or SAML authentication? enabled, select OIDC and Client type Web app, and enter the web app's Redirect URIs.
- Login Experience: select Journey-orchestrated, the SSO client group of the client's own Mosaic application, and the SSO journey from Step 2. For Mosaic-hosted screens, select a Style or use the default Mosaic style. See Manage styling for the Mosaic-hosted SSO experience.
- Advanced settings: choose the client authentication method and review token lifetimes. See OIDC advanced settings.
- Client roles: select the roles the client needs to call Mosaic APIs. If you don't select a role, the client implicitly receives the App Admin role. See Manage client roles.
Save the client. Mosaic generates the client ID and the credentials for the selected authentication method; they're available from the client details page. For all fields, see Configure an OIDC client.
Integrate each app with its own client, using the tab that matches its type.
Send an authorization request with the client ID and redirect URI, exchange the returned code for user tokens from your backend, and validate the tokens before creating the app's local session. See Launch OIDC SSO with the Mosaic-hosted experience and Validate tokens.
If an SSO client group uses Self managed (Custom UI), build the login page with the Mosaic Platform SDK, which runs the SSO journey, and host it at the group's Login page URL. See Build your SSO page.
Implement session renewal and logout within each Mosaic application's scope. Follow SSO session logout for browser SSO or Manage backend sessions for backend-based login.
To test isolation, use a test user in each Mosaic application. Create them from Users > + Add Users, enter an email address, and select only that user's Mosaic application. See Manage users. A login method based on email OTP can sign these users in; for passwords or passkeys, each user must register the credential first.
- A user who signs up in one app has no account in the other app until they register there.
- Credentials, such as passwords or passkeys, registered in one app can't be used in the other.
- Signing in to one app doesn't create a session for the other.